Splendid Isolation

Little Brother

It’s one thing to have to deal with the Gummint snooping on your every move — literal, and figurative (i.e. your online activities) — but it’s another thing to having GlobalMegaCorp sniffing into your business as well.

Here’s how all this started:

Ruter, the [Norwegian] transit authority that runs public buses across Oslo and Akershus, parked two electric buses inside an isolated facility built into a mountain, the kind of shielded space normally used to keep radio signals from leaking in or out, and let its own security engineers take them apart. One bus came from Yutong, the Chinese manufacturer that has quietly become one of Europe’s largest electric bus suppliers. The other was a three-year-old unit from VDL, a Dutch manufacturer. Ruter chose that pairing deliberately: the two buses sit at opposite ends of how connected a modern transit vehicle can be.

And the findings?

Ruter’s own published findings are blunt about the VDL [Dutch] bus: it has no capability for over-the-air software updates at all. Every change to its systems requires a technician to physically connect a cable. That makes it a hassle to service. It also makes it nearly impossible to hijack remotely, which is exactly why Ruter’s engineers moved past it quickly.

The Yutong [Chinese] bus is the opposite. It receives software and diagnostic updates automatically, the same way a phone downloads a firmware patch overnight, except this particular phone weighs roughly 30,000 pounds and carries dozens of passengers through Oslo traffic. That connection routes through a Romanian SIM card, which gives Yutong direct digital access to the bus’s battery and power management systems. Ruter’s engineers concluded that, in theory, this access could be used to stop the bus or render it inoperable, not through some elaborate hack, but simply because the manufacturer already has a standing door into those systems for legitimate diagnostic and update purposes.

Wile all this is alarming, it’s not really surprising.  We’ve known for ages that the godless ChiCommies have their dirty little ears glued to just about every damn piece of electronic equipment our friends (!) in Silicon Valley have outsourced to their manufacture.

So now we get to the part that makes me start fixing a lunch bucket, scoping out high buildings and cleaning the Mauser.

None of what Ruter found is exotic. It’s the standard architecture of any modern connected vehicle, and American drivers have been living with a version of it for nearly two decades. General Motors’ OnStar system can, at the company’s discretion, send a cellular command to a stolen vehicle that blocks the ignition from restarting once it’s parked, or gradually slows a moving vehicle so police can recover it safely. That is functionally the same category of access Ruter found in the Yutong bus: a persistent, manufacturer-controlled cellular link with authority over propulsion-adjacent systems, built into the vehicle before it ever reaches a customer’s driveway.

So Big Auto are a bunch of snooping smegma-eaters.  We know that, too.

The distinction that actually matters here isn’t whether a manufacturer can reach into a vehicle remotely. Almost every connected car sold today allows that, by design, for updates, diagnostics, and theft recovery. What matters is who holds the authority to use that access, under what legal process, and how many vehicles go dark at once if that access is ever misused, subpoenaed, or compromised.

A single stolen sedan getting slowed to a stop by its own manufacturer is a feature working as intended. An entire transit authority’s bus fleet answering to a remote command from a foreign supplier’s server is a different order of risk entirely, which is exactly why Ruter escalated this to Norway’s national government instead of treating it as an IT ticket.

Now comes the part that has me checking Ye Olde Ammoe Locquer for 8x57mm:

Chinese abuse of this little backdoor activity [sic] is bad, but in the bigger picture, it can be addressed with a carefully-aimed chunk or two of explosive material on the Three Gorges Dam.

What worries me more is that this little pipeline into our cars can also be — and is — at the beck and call of the auto manufacturers, who are only too ready to “share” that data with, say, the insurance industry (hello, fresh revenue stream), and if pressed just a little, with our own Gummint ghouls who infest the alphabet agencies (DHS, NSA, FBI, just to name the three biggest dicks aimed at out collective rectums).

I need to get to the range.  So if you’ll excuse me…
 

Private & Personal

I’ve never been that interested in my origins to have done the 23andMe thing, so I’m personally not affected by this activity.  Nevertheless:

Twenty-seven states and the District of Columbia have sued the genetic-testing company 23andMe to oppose the sale of DNA data from its customers without their direct consent.

The suit, filed on Monday in U.S. Bankruptcy Court in the Eastern District of Missouri, argues that 23andMe needs to have permission from each and every customer before their data is potentially sold. The company had entered an agreement to sell itself and its assets in bankruptcy court.

The information for sale “comprises an unprecedented compilation of highly sensitive and immutable personal data of consumers,” according to the lawsuit.

The genetic data at stake is especially sensitive and should be protected, because if it is stolen or compromised, it cannot be replaced. The data can be used to track not only the individuals who sent the kits, but also people related to customers, including yet unborn generations.

Why, and who is the prospective purchaser of all this “highly sensitive and immutable personal data”, you ask?

[23andMe] is poised to be acquired by Regeneron Pharmaceuticals for $256 million, according to the lawsuit.  Regeneron is a biotechnology company that uses genetic data to develop new drugs.

So there’s no chance that the data will be abused in any way, then. [eyecross]

I think that my position on this kind of thing should be fairly obvious by now.

Your personal data — all of it — belongs to you, and to nobody else.  Only you can authorize its use or dissemination, for whatever reason.

So if some asshole organization — let’s just call them Regeneron, for brevity’s sake — wants to use personal (i.e. unaggregated) data, they should have to ask you personally for your permission, each and every time.  (Once data is aggregated, of course, your anonymity is no longer an issue.)


By the way, the same should apply to US Census data, but that particular bullet has gone through the church countless times already, and it’s a terrible precedent.  (Which is why I always urge people not to fill out the “long form” census questionnaire every time this bit of government snoopery comes around.)

Same Here

Tom Knighton has written an article which resonates with me, for obvious reasons:

By now, we’re all well aware of the Biden-era “Strategic Implementation Plan for Countering Domestic Terrorism,” which has some very troubling language in it.

As Just the News reported earlier on Tuesday, the criteria included buying guns, being a veteran, and what was termed as “‘xenophobic’ disinformation.”

I’m a veteran and gun owner, and I was pretty critical of China during the whole pandemic, at least on social media. Now, I’m curious as to whether my own government was monitoring my lawful activity simply because I wasn’t a raging leftist loon willing to toe the progressive party line on these issues.

Was I considered a threat to become a domestic terrorist?

Anyone see any parallels between Knighton and me?  The only difference between us is that I’m a veteran of another country’s army — but I’m still a veteran.  (As for the criticism of the foul ChiComs, and buying guns:  ipse dixit.)

I have no idea what is/was meant by “xenophobic disinformation”, but if it means saying that I heartily dislike furriners who creep illegally over our borders to take jobs away from U.S. citizens, commit other crimes, engage in espionage or otherwise try to undermine our country, then I’d have to plead nolo contendere*.

Knighton goes on:

I’m sure I could file a FOIA request and find out, and part of me is considering doing just that, but another part of me would rather not know.

I do have one hint that I may be on such a list if “undesirables”:  back in 2017 (that would have been under the Obama administration), I had the dreaded “SSSS” designation appear on one of my air tickets, but it was for one flight only (among several others in that year and the year following), and Obama had only been  in  out of power for a few months at that point.

I’m fairly sure  that I was “noted” by some government apparatchik during the latter years of his presidency, and if not then, I have absolutely no doubt that I was flagged during the Biden era.

This website is my only “online presence” (no Twatter, no Fecesbook, no Instagram and certainly no ChiCom-based Tik Tok either), but over the years several of my posts have engendered (shall we say) some notoriety, and it wouldn’t take much for those to have got me noted and monitored by some DHS/FBI drone.

Anyway, my interest in such surveillance by the .gov is minimal, although I am a kindred spirit of Tom Knighton’s in that:

Finding out that I was monitored because of my views and lawful behavior might just be too much for me to tolerate, and I’m seeing too much that I’m incapable of tolerating as it is.

Amen, Brother Tom.

And now, if you’ll excuse me, I’m off to the range.  My AK-47 is feeling all neglected and stuff.


*Whole lotta Latin in this post… sorry.

Surveillance

Seems as though you can’t do anything these days without being spied on by the fucking Government:

Recent revelations confirm that the Bureau of Alcohol, Tobacco, Firearms, and Explosives has been aggressively expanding its use of facial recognition technology, raising significant concerns about mass surveillance and unconstitutional tracking of law-abiding gun owners.

For years, gun rights advocates have warned that the ATF’s use of facial recognition would lead to mass surveillance of American citizens—particularly those who exercise their Second Amendment rights. Despite repeated claims that the ATF doesn’t engage in biometric tracking, a 2021 Government Accountability Office report revealed that between October 2019 and March 2022, the ATF conducted at least 549 facial recognition searches.

Of course, it’s not actually the ATF doing this (a.k.a. plausible deniability):

The technology was largely powered by third-party vendors, including Clearview AI and Vigilant Solutions, both of which have amassed vast databases of billions of images scraped from social media, DMV records, and security footage. This means the ATF has been leveraging private sector databases to track and identify gun owners without their consent.

The full scale of this surveillance remains unclear, but newly surfaced documents indicate that the ATF has been working with FBI fusion centers, state and local law enforcement, and even foreign intelligence agencies to develop more comprehensive tracking capabilities.

Here’s the thing:  I don’t want to be spied on by anyone, let alone these government thugs.

I don’t care that it helps “security” or any other such panacea.  Take your snooping devices and go fuck yourselves.

That said:

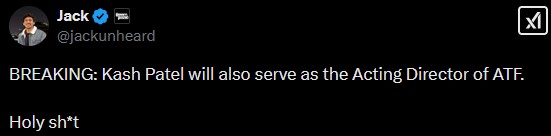
Oh, and new-FBI Director / ATF Acting-Director Patel?  Take a long, hard look at those “FBI fusion centers” and make them less malevolent — lest you too be labeled as just another government thug.

Information, we’re always being told, is power.  And I want the government to have a lot less of both.

Some Detail Required

In the above post, I refer to the FBI “fusion centers”.  For those who went “Huh?” at the term, here’s a good background piece, framed inside an overall theme of the militarization of the police (which I’ve ranted about often before, as it happens).  Here’s an excerpt:

Fusion Centers are hubs for local, state and federal police to share information. They’re effectively intelligence-gathering done by various police agencies who pool their resources. While this isn’t an uncommon practice, the Fusion Centers have virtually no oversight and are filled with zeal for the War on Terror. While its primary existence was to surveil in the fight against terrorism, Fusion Centers have quickly ballooned to gather intelligence on just about anything – and it’s not just the police. The military participates in Fusion Centers, as does the private sector, which means they’re a privacy nightmare.  

The federal government has pushed Fusion Centers and largely bankrolled them. Hundreds of FBI agents work with Fusion Centers, with the federal government providing hundreds of millions of dollars in federal aid. In the case of the Maryland Coordination and Analysis Center, the federal government created a Fusion Center at the state level, only eventually turning control of an ostensibly state agency to the state. 30 percent of these “state” agencies are physically located in federal office space.

Private sector companies collect, store and analyze data for Fusion Centers. This would be dangerous on its own, but the lack of any oversight makes it particularly troublesome. Even if a private sector has the best of intentions, malicious third-party actors could access some of your most sensitive data if it’s been datamined by a Fusion Center. A company without the best intentions can do all kinds of “government-approved” snooping into your personal affairs.

And there you have it, in a nutshell.

Read the whole thing, because while it may contain a whole bunch of stuff you already know about, there’s no harm in being reminded about it, as I was.

Snoops

Yeah, don’t fuck mess with Texas:

Texas has sued insurance provider Allstate, alleging that the firm and its data broker subsidiary used data from apps like GasBuddy, Routely, and Life360 to quietly track drivers and adjust or cancel their policies.

Allstate and Arity, a “mobility data and analytics” firm founded by Allstate in 2016, collected “trillions of miles worth of location data” from more than 45 million people, then used that data to adjust rates, according to Texas’ lawsuit. This violates Texas’ Data Privacy and Security Act, which requires “clear notice and informed consent” on how collected data can be used. A statement from Texas Attorney General Ken Paxton said the suit is the first-ever state action targeting comprehensive data privacy violations.

How so?

According to Texas’ complaint (PDF), the data collected included “a phone’s geolocation data, accelerometer data, magnetometer data, and gyroscopic data, which monitors details such as the phone’s altitude, longitude, latitude, bearing, GPS time, speed, and accuracy.”

With that data—plus, in some cases, data from connected vehicles—Allstate could see when, how far, and for how long someone was driving, along with “hard braking events” and “whether a consumer picked up or opened their phone while traveling at certain speeds.”

Texas’ lawsuit claims that Arity incentivized—through “generous bonus incentives”—apps like GasBuddy, a gas price-tracking app, and Life360, which is intended to keep tabs on family members’ location, to “increas[e] the size of their dataset.” Under their agreements with app makers, Arity had “varying levels of control over the privacy disclosures and consent language” shown to app users, according to the complaint.

And now for the doublespeak:

“Arity helps consumers get the most accurate auto insurance price after they consent in a simple and transparent way that fully complies with all laws and regulations.”

But they’re not the only villains in this piece:

The suit also cites Allstate as gathering direct car use data from Toyota, Lexus, Mazda, Chrysler, Dodge, Fiat, Jeep, Maserati, and Ram vehicles.

And if these assholes shared data with Allstate, you can bet your house that they did so with other insurance companies too.

If you’re not into letting corporations do this to you:

…you may want to avoid any dealings at all with these bastards.  It’s not like Stellantis (Chrysler, Dodge, Fiat, Jeep, Maserati) are reporting a boom in sales, after all.

When the Texans win their suit, at it should, I would argue against fines because those bastards will just pass the cost into their customers and claim a tax deduction at worst.

What I would do as TxAG is get a list of all Texans with Allstate policies, and demand that Allstate provide free insurance to them for a period of time commensurate with the start date of Arity’s snoopery.

I know, that would just cause Allstate to cease operations in Texas.  That’s fine, too — take away access to the second-largest pool of drivers in the U.S.